


Latest Feb 19, 2022 Real SC-200 Exam Dumps Questions Valid SC-200 Dumps PDF
Microsoft SC-200 Exam Dumps - PDF Questions and Testing Engine
How to Register For Exam SC-200: Microsoft Security Operations Analyst?
NEW QUESTION 47
You need to modify the anomaly detection policy settings to meet the Cloud App Security requirements.
Which policy should you modify?
- A. Activity from suspicious IP addresses
- B. Impossible travel
- C. Activity from anonymous IP addresses
- D. Risky sign-in
Answer: B
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/cloud-app-security/anomaly-detection-policy
NEW QUESTION 48
You need to assign a role-based access control (RBAC) role to admin1 to meet the Azure Sentinel requirements and the business requirements.
Which role should you assign?
- A. Automation Runbook Operator
- B. Logic App Contributor
- C. Automation Operator
- D. Azure Sentinel Contributor
Answer: D
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/roles
NEW QUESTION 49
You use Azure Security Center.
You receive a security alert in Security Center.
You need to view recommendations to resolve the alert in Security Center.
What should you do?
- A. From Regulatory compliance, download the report.
- B. From Security alerts, select the alert, select Take Action, and then expand the Prevent future attacks section.
- C. From Recommendations, download the CSV report.
- D. From Security alerts, select Take Action, and then expand the Mitigate the threat section.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-managing-and-responding-alerts
NEW QUESTION 50
You create an Azure subscription named sub1.
In sub1, you create a Log Analytics workspace named workspace1.
You enable Azure Security Center and configure Security Center to use workspace1.
You need to collect security event logs from the Azure virtual machines that report to workspace1.
What should you do?
- A. In sub1, register a provider.
- B. From Security Center, create a Workflow automation.
- C. From Security Center, enable data collection
- D. In workspace1, create a workbook.
Answer: C
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-enable-data-collection
NEW QUESTION 51
You have a Microsoft 365 E5 subscription that uses Microsoft Defender and an Azure subscription that uses Azure Sentinel.
You need to identify all the devices that contain files in emails sent by a known malicious email sender. The query will be based on the match of the SHA256 hash.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.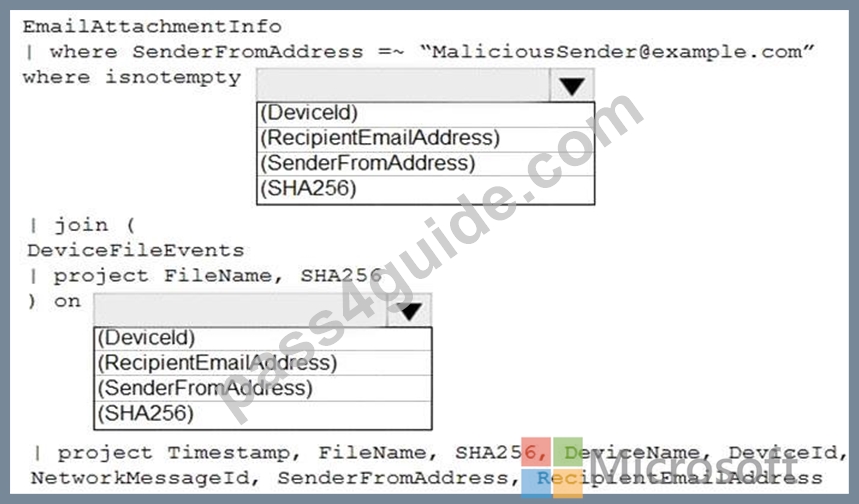
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated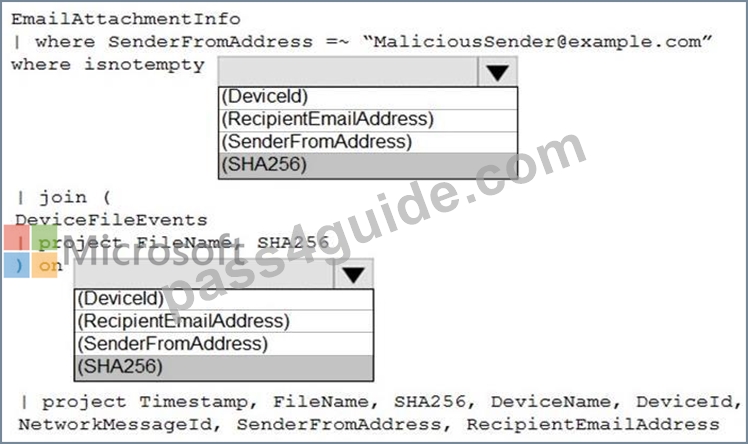
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/advanced-hunting-query-emails-devices?view=
NEW QUESTION 52
You open the Cloud App Security portal as shown in the following exhibit.
You need to remediate the risk for the Launchpad app.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.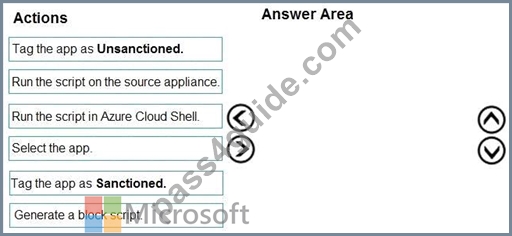
Answer:
Explanation:
Explanation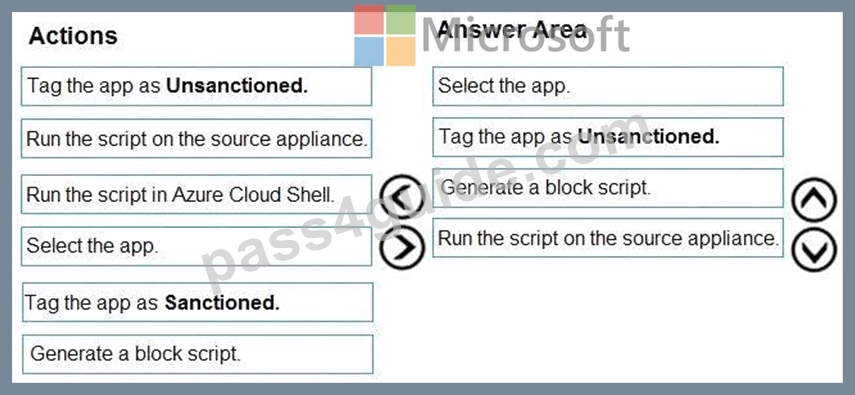
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/governance-discovery
NEW QUESTION 53
You have an Azure Sentinel deployment in the East US Azure region.
You create a Log Analytics workspace named LogsWest in the West US Azure region.
You need to ensure that you can use scheduled analytics rules in the existing Azure Sentinel deployment to generate alerts based on queries to LogsWest.
What should you do first?
- A. Create a data connector in Azure Sentinel.
- B. Deploy Azure Data Catalog to the West US Azure region.
- C. Add Azure Sentinel to a workspace.
- D. Modify the workspace settings of the existing Azure Sentinel deployment
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/extend-sentinel-across-workspaces-tenants
NEW QUESTION 54
You plan to create a custom Azure Sentinel query that will provide a visual representation of the security alerts generated by Azure Security Center.
You need to create a query that will be used to display a bar graph.
What should you include in the query?
- A. count
- B. extend
- C. bin
- D. workspace
Answer: A
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/visualize/workbooks-chart-visualizations
NEW QUESTION 55
You have resources in Azure and Google cloud.
You need to ingest Google Cloud Platform (GCP) data into Azure Defender.
In which order should you perform the actions? To answer, move all actions from the list of actions to the answer area and arrange them in the correct order.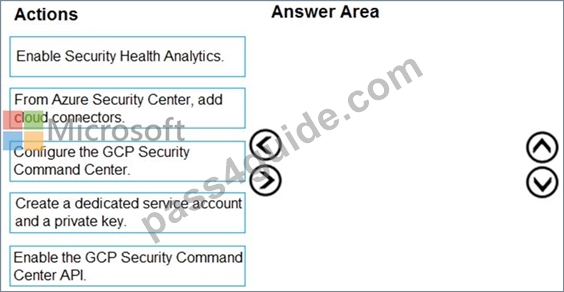
Answer:
Explanation: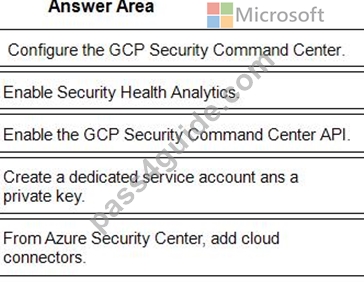
1 - Configure the GCP Security Command Center.
2 - Enable Security Health Analytics.
3 - Enable the GCP Security Command Center API.
4 - Create a dedicated service account ans a private key.
5 - From Azure Security Center, add cloud connectors.
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-onboard-gcp
NEW QUESTION 56
Your company uses Azure Security Center and Azure Defender.
The security operations team at the company informs you that it does NOT receive email notifications for security alerts.
What should you configure in Security Center to enable the email notifications?
- A. Azure Defender
- B. Pricing & settings
- C. Security policy
- D. Security alerts
- E. Security solutions
Answer: B
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-provide-security-contact-details
NEW QUESTION 57
You plan to connect an external solution that will send Common Event Format (CEF) messages to Azure Sentinel.
You need to deploy the log forwarder.
Which three actions should you perform in sequence? To answer, move the appropriate actions form the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: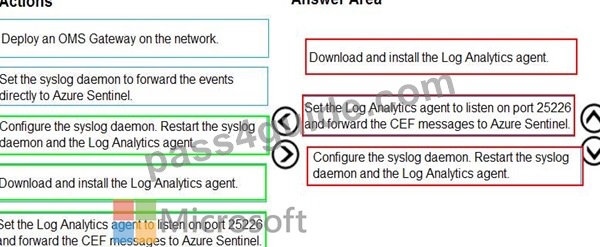
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-cef-agent?tabs=rsyslog
NEW QUESTION 58
You deploy Azure Sentinel.
You need to implement connectors in Azure Sentinel to monitor Microsoft Teams and Linux virtual machines in Azure. The solution must minimize administrative effort.
Which data connector type should you use for each workload? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.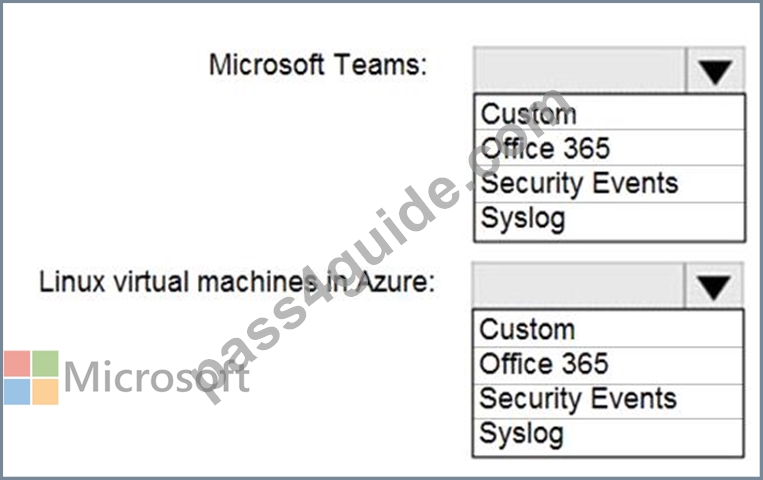
Answer:
Explanation: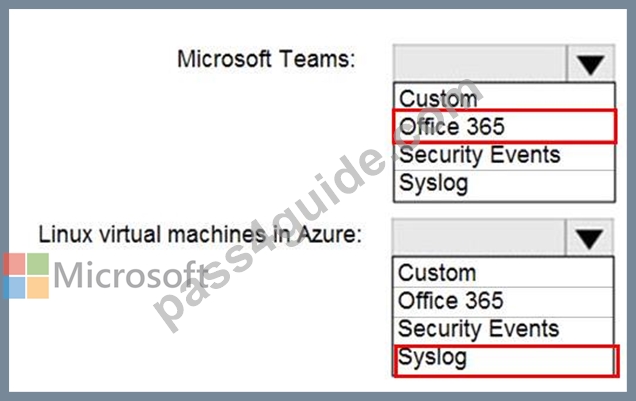
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-office-365
https://docs.microsoft.com/en-us/azure/sentinel/connect-syslog
NEW QUESTION 59
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: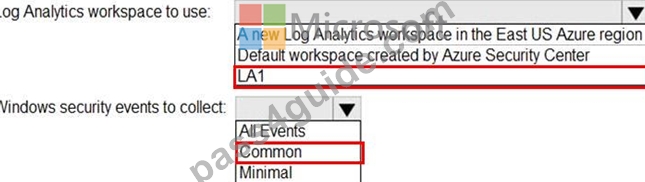
NEW QUESTION 60
You need to implement the Azure Information Protection requirements.
What should you configure first?
- A. Device health and compliance reports settings in Microsoft Defender Security Center
- B. scanner clusters in Azure Information Protection from the Azure portal
- C. content scan jobs in Azure Information Protection from the Azure portal
- D. Advanced features from Settings in Microsoft Defender Security Center
Answer: D
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/information- protection-in-windows-overview
NEW QUESTION 61
Your company uses Microsoft Defender for Endpoint.
The company has Microsoft Word documents that contain macros. The documents are used frequently on the devices of the company's accounting team.
You need to hide false positive in the Alerts queue, while maintaining the existing security posture.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Resolve the alert automatically.
- B. Generate the alert.
- C. Create a suppression rule scoped to any device.
- D. Create a suppression rule scoped to a device group.
- E. Hide the alert.
Answer: B,C,E
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/manage-alerts
NEW QUESTION 62
You receive a security bulletin about a potential attack that uses an image file.
You need to create an indicator of compromise (IoC) in Microsoft Defender for Endpoint to prevent the attack.
Which indicator type should you use?
- A. a URL/domain indicator that has Action set to Alert and block
- B. a certificate indicator that has Action set to Alert and block
- C. a file hash indicator that has Action set to Alert and block
- D. a URL/domain indicator that has Action set to Alert only
Answer: C
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/indicator-file?view=o365-worldwide
NEW QUESTION 63
You have an existing Azure logic app that is used to block Azure Active Directory (Azure AD) users. The logic app is triggered manually.
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel. What should you do first?
- A. Configure a custom Threat Intelligence connector in Azure Sentinel.
- B. Modify the trigger in the logic app.
- C. And a new scheduled query rule.
- D. Add a data connector to Azure Sentinel.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/playbook-triggers-actions https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
NEW QUESTION 64
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Azure Sentinel.
You need to create an incident in Azure Sentinel when a sign-in to an Azure virtual machine from a malicious IP address is detected.
Solution: You create a Microsoft incident creation rule for a data connector.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-azure-security-center
NEW QUESTION 65
You need to visualize Azure Sentinel data and enrich the data by using third-party data sources to identify indicators of compromise (IoC).
What should you use?
- A. Microsoft Cloud App Security
- B. Azure Monitor
- C. notebooks in Azure Sentinel
- D. hunting queries in Azure Sentinel
Answer: C
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/notebooks
NEW QUESTION 66
HOTSPOT
You have an Azure subscription that has Azure Defender enabled for all supported resource types.
You create an Azure logic app named LA1.
You plan to use LA1 to automatically remediate security risks detected in Azure Security Center.
You need to test LA1 in Security Center.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: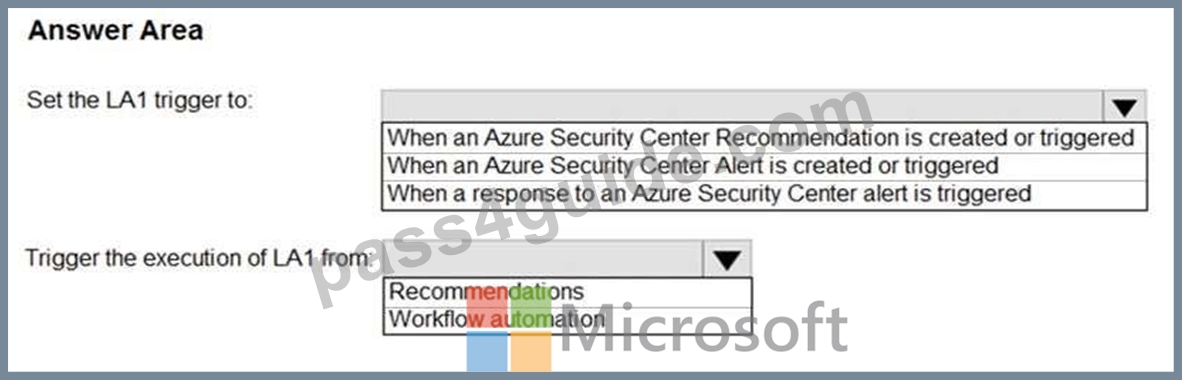
Answer:
Explanation: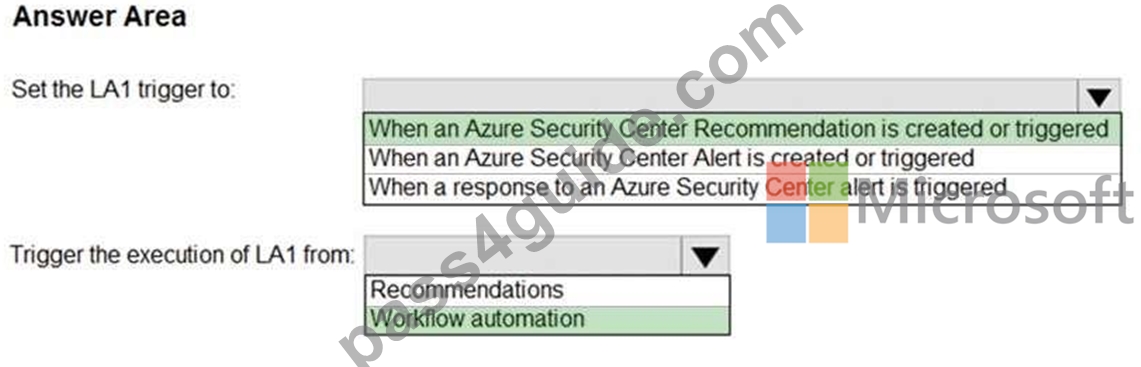
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/security-center/workflow-automation#create-a-logic-app-and-define- when-it-should-automatically-run
NEW QUESTION 67
You need to configure the Azure Sentinel integration to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.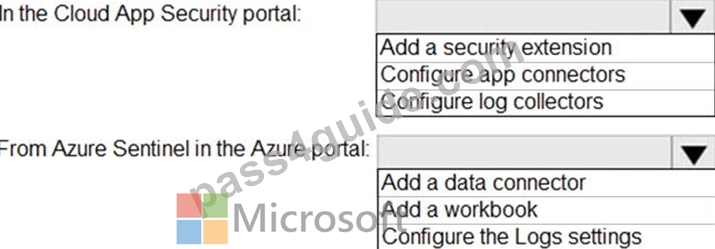
Answer:
Explanation: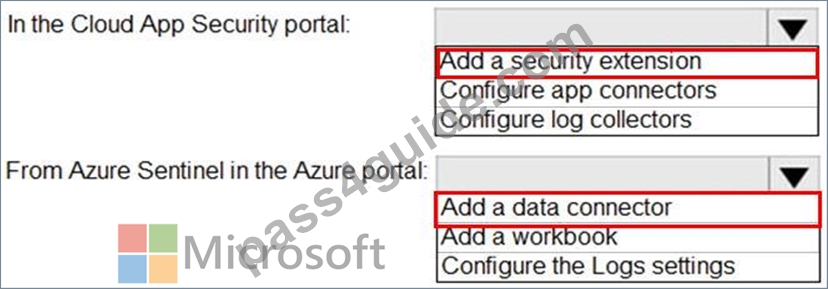
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/siem-sentinel
NEW QUESTION 68
......
Reliable Microsoft Certified: Security Operations Analyst Associate SC-200 Dumps PDF Feb 19, 2022 Recently Updated Questions: https://prepcram.pass4guide.com/SC-200-dumps-questions.html